G DATA Managed XDR
Role Management
Roles define the set of permissions users need to perform their assigned tasks. Roles reflect how responsibilities are organized in your company.
|
We recommend using the predefined roles Admin and Read-Only. |
If needed, you can create custom roles for each category and assign them to users.
During the Kick-off, our G DATA Security Operations Team advises you on designing a suitable role structure.
The overview shows the available categories. The categories displayed depend on the products assigned to your Organization Unit. When you subscribe to additional products, the corresponding categories are added automatically.

Overview
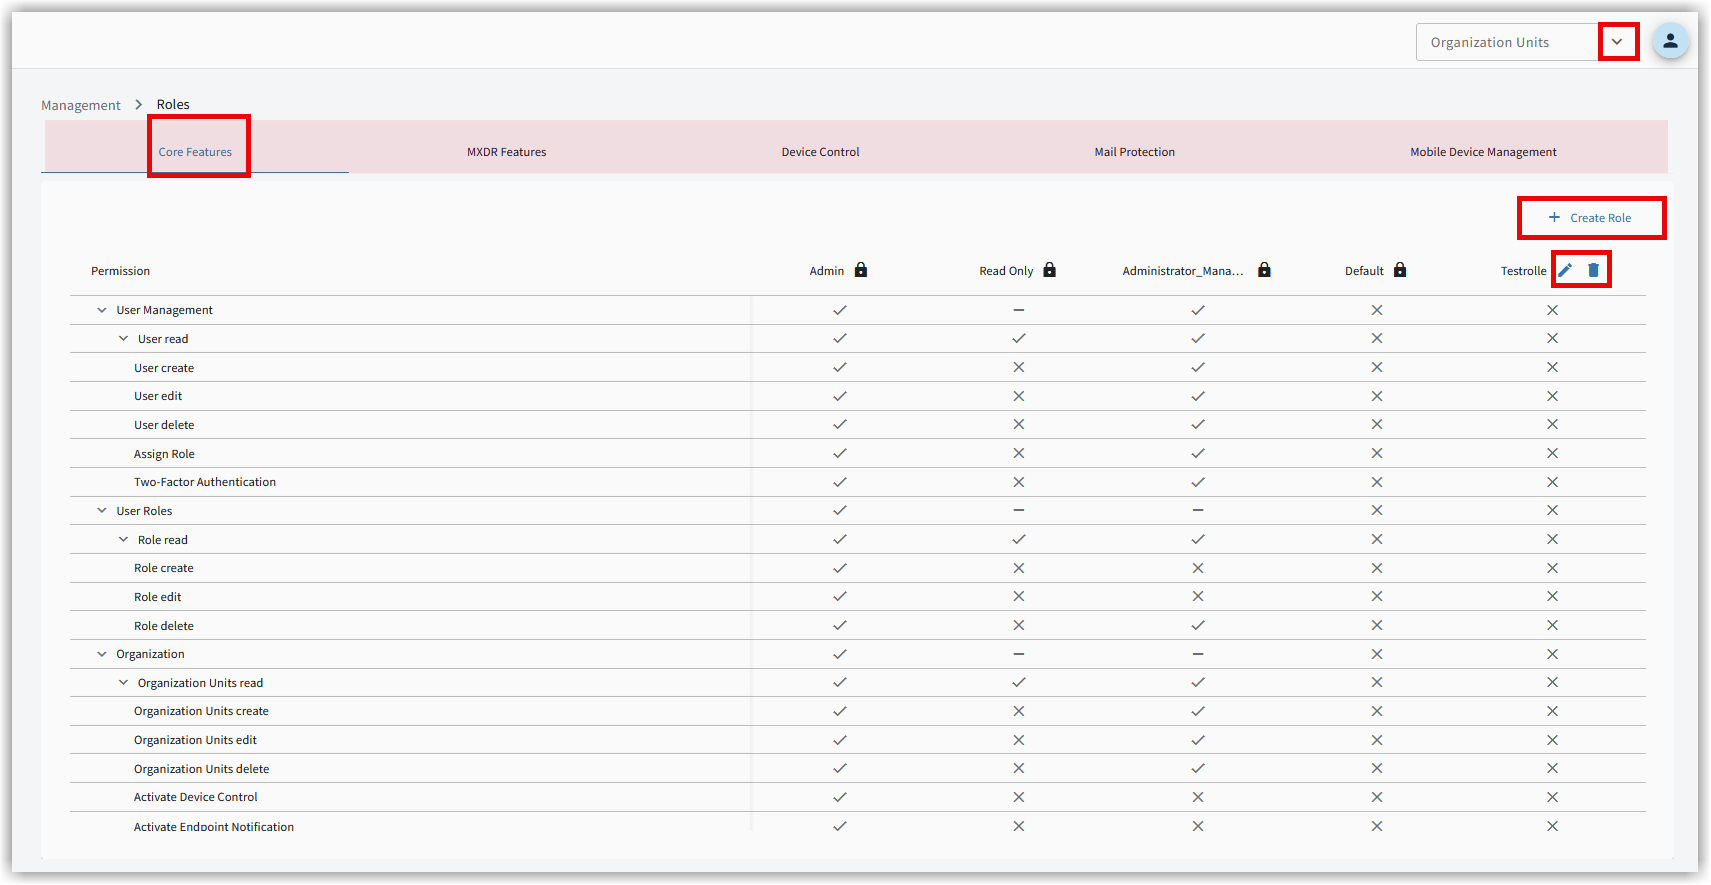
Role management shows the permission assignments for the generic roles Admin and Read Only. These roles
cannot be removed. If needed, custom roles can be created for each category using
 .
The window for assigning permissions to the new role opens.
To change the permissions of a custom role, click in the corresponding row on the edit icon  .
To delete a role, click the delete icon in the corresponding row
 .
|
A role can only be deleted when it is no longer assigned to any users. During deletion, a new role can be assigned to the affected users. 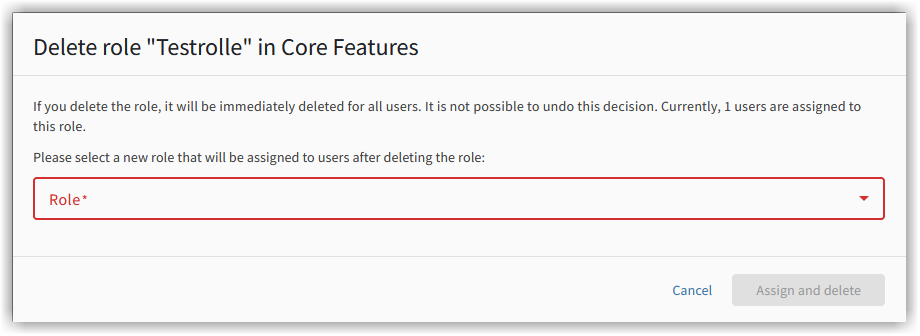
|
Core Functions
Core Functions
Core functions support general operation of the web portal and provide capabilities for User Management, User Roles, and Organization. The available permissions are listed below by category.
User Management
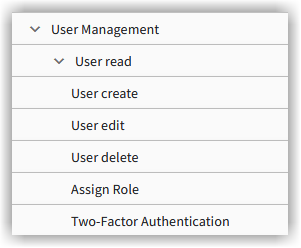
View Users |
Allows viewing users. |
Create Users |
Allows creating new users. |
Edit Users |
Allows editing existing users. |
Delete Users |
Allows deleting existing users. |
Assign a Role |
Allows assigning a role to a user. |
Two-Factor Authentication |
Permission to enable or disable two-factor authentication for a user. |
User Roles
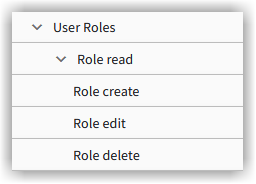
View Roles |
Allows viewing roles. |
Create Roles |
Allows creating new roles. |
Edit Roles |
Allows editing existing roles. |
Delete Roles |
Allows deleting existing roles. |
Organization
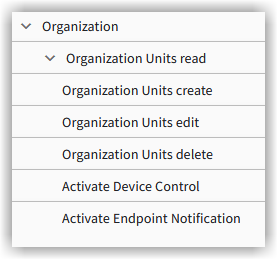
View Organization Units |
Permission to view Organization Units. |
Create Organization Units |
Allows viewing Organization Units. |
Edit Organization Units |
Allows editing existing Organization Units. |
Delete Organization Units |
Allows deleting existing Organization Units. |
Enable Device Control |
Allows enabling Device Control. |
Enable Endpoint Notifications |
Allows assigning Endpoint notifications. |
MXDR Functions
G DATA Managed XDR
MXDR Functions
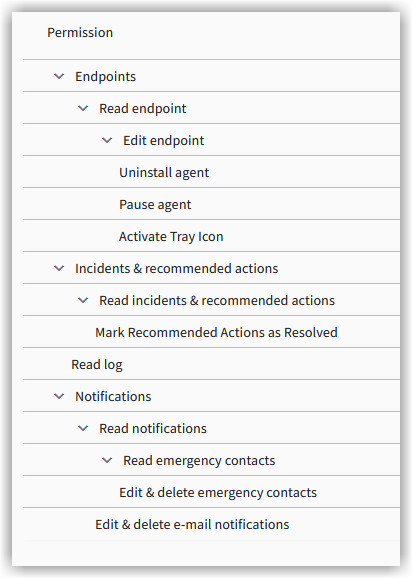
View and Edit |
Specifies whether users with this role can view and/or edit Endpoints. |
||
Agent Settings |
Removing an Endpoint from the portal requires permission to uninstall Agents from Endpoints. When starting the Agent uninstallation, you can choose whether to remove the Endpoint record from the portal at the same time. Users authorized to uninstall Agents can also remove the Endpoint record from the G DATA Web Portal later.
|
||
Pause Agent |
Specify whether users with this role can pause the Agent on Endpoints for 15 minutes.
|
||
Enable Tray Icon |
Specify whether users with this role can display the Agent icon in the Windows notification area on Endpoints. |
Incidents & Recommended Actions
View Incidents & Recommended Actions |
Specify whether users with this role can view Incidents and Recommended Actions. |
Mark Recommended Actions as Complete |
Specify whether users with this role can mark Recommended Actions as complete. This option is available only if the role has permission to view Recommended Actions. |
View Logs |
Specify whether users with this role can access the Logs view. |
Notifications
View Notifications |
Switch that controls whether users with this role receive notifications. |
||
Edit & Delete Emergency Contacts |
Specify whether users with this role can add users to and remove users from the emergency contact list.
|
||
Edit & Delete Email Notifications |
Specify whether users with this role can add users to and remove users from the email notification recipient list. You can also set the email language and the types of notification events.
|
Device Management
Device Management
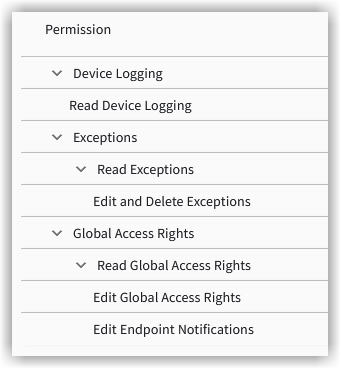
If you use G DATA Policy Control, you can specify here which changes users with this role can make in the product.
Device Activity Logging |
Specifies whether users with this role can view device activity logs. |
View Exclusions |
Allows viewing Exclusions. |
Edit and Delete Exclusions |
Allows editing and deleting Exclusions. |
Global Access Rules |
Specifies whether users with this role can view and/or edit global access rules and edit the notifications displayed on Endpoints. |